















Zero knowledge proofs enable trustless integration of hidden information into blockchain applications by allowing provers to demonstrate the validity of private data without revealing it; in this tutorial, the Circom/SnarkJS stack generates Solidity verifiers that accept public inputs (like board hashes and shot coordinates) while keeping the underlying game state private, enabling privacy-preserving features such as gasless transactions via meta-transactions and social sign-on through services like Taurus and Biconomy.
Zero Knowledge Proofs in Solidity: SnarkJS Verifiers Tutorial
Added:Basic understanding of Zero-Knowledge Proofs (ZKPs), specifically the conceptual roles of the Prover, Verifier, and Witness in zk-SNARKs.
Proficiency in Solidity smart contract development, including writing, deploying, and testing contracts on EVM-compatible networks.
Familiarity with JavaScript/Node.js environments, as SnarkJS is a JS-based library used for generating proofs and verifier contracts.
Understanding of the ERC-2771 standard for meta-transactions and trusted forwarders to facilitate gasless or mediated transactions.
Basic knowledge of ZK-friendly cryptographic hashing algorithms, such as Poseidon or MiMC, which are commonly used to commit to private state.
Writing custom arithmetic circuits using Circom to define complex private logic and constraint systems for your decentralized applications.
Advanced gas optimization techniques for on-chain verification, including utilizing EVM elliptic curve precompiles and batch verification.
Designing secure client-side proof generation pipelines to ensure user privacy is maintained entirely locally before submitting verification proofs.
Exploring alternative Zero-Knowledge development frameworks and domain-specific languages such as Noir, Leo, or Halo2.
Architecting full-scale decentralized, incomplete-information games (e.g., fog-of-war games) using zk-SNARKs and state synchronization.
2.1K views32likes14:05Original Release: 2022-03-12
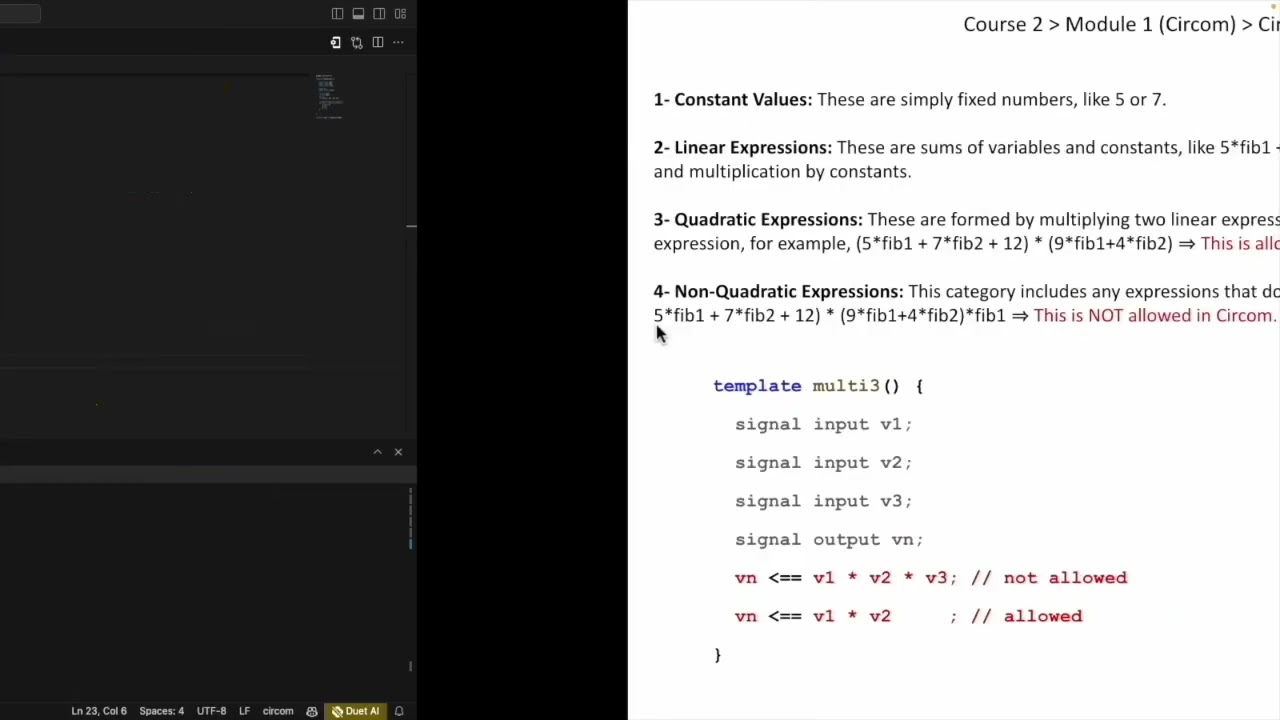
and what we have is the zero knowledge which goes here a b and c and we'll get to a little issue we have with subgraphs and how we get around it um with the 2d array in b and then your input your public input this is where the magic of zero knowledge and privacy comes in we will be showing you how we how we trustlessly enable provable integration of hidden information into your game by using these inputs and if we go really quickly just to give you a taste of the circom we have board verifier and let's go to board and you can see that if we scroll down all the way here there is a single public input and that is hash right um and we'll get back to what all this means in a second and for shot there's hash shot and hit which is three inputs but if we go look at shot it's actually two different numbers so going back to i verifier we have four different unsigned 256-bit integers that we want to pass into the proof along with our our zero knowledge proof as a trustless computation and this allows us by having this definition of our interfaces like this allows us to extend the verifiers in our code even before we have generated it through the yarn setup command and if we go look at the verifiers themselves i'm i'm not even going to get into it but you don't have to either it's the thing this is all handled by snark js um the galaxy brand jordy balina and his team of course and the contributions of a lot of other people you know but they've built this automated tool that will handle all of your proving you just need to give it the inputs but it looks very daunting but if you come across this it really isn't that bad just don't think about it so then we have a minimal trusted forwarder set up so that we can do gasless transactions we want to do bikonomy and taurus which is a social sign-on to allow people to sign in with twitter or google and still also be able to pay without any gas or anything like that so by using taurus and biconomy in combination along with all of these other mechanics and privacy and scalability we can really approach a web 2 experience on web3 and this requires some signature stuff but we we have all of that it's very easily copyable the only difference you're ever going to see with erc2771 is going to be instead of using [Music] message.sender you're going to use underscore message sender the function and this will first check if it's a meta transaction if it's capable of relaying it from a signature and if it's not it will fall back on message sender now on to the interface where essentially we just extend the meta transactions and the verifiers so we have all our events um and we basically emit all the information we need for the subgraph to index all of this stuff so we have uh the game structs which contains a lot of important information but there probably is a little bit of information that we could cut from this and basically how it works is this hit max right here five four three three two sums to 17 it tracks the hit nonce and whenever it gets to 17 we expect the game to be over game index to just be announced for making new games um and okay so here we can see b0 b1 and this is done because the sub graph did not like having to index contracts that had parameters that were 2d arrays so the subgraph won the argument so let's go into the actual code as we start to really get into the functionality even though it's all documented in there so the very first thing we have are the modifiers and i'm not going to go super in depth into all of these because a lot of this is more so just solidity but for turns we basically just use the modulus of two if it's zero it should be the player who hosted the game's turn and if it's one it should be the player who joined the game's turn um and yeah the rest of this is just solidity so so for the constructor and we'll walk through very quickly our hard hat deploy file we have our forwarder which just points to a dichotomy forwarder as well as the two verifiers that we deploy and again by using that pattern of having the verifier interfaces defined we can use them in our code without actually having them generated so what we've done throughout all of this is we've taken out the input section in proofs and instead we passed those in within the scope of our own solidity and that's done basically mentally to put ourselves in the mindset that those inputs are generated somewhat trustlessly so um not always will all of the inputs come from the parameters in here and we'll get to that in a second for new game we see that the very first thing we have to do is verify the proof and that entails taking all of the parameters that go into this function and all the zero knowledge proof goes in we massage the subgraph compliant parameters into something that the verifier will understand and then we pass in the input which in our case is just the board hash and this board hash serves as a proof that this hash is of a valid board configuration and we will then store this in the game struct for future use and it'll be associated with this user so for join game we have the same thing as new game board hash and the zero knowledge proof as well as an index of a game which serves as a game room for a new game or if the game's already started allows you to point at it and get data so functionally the same thing happens here though so there are a couple of interesting properties of how this works that introduced some kind of perverse uh incentives in the game theory that we don't actually solve we we assume honest actors and there are totally solutions but we'll get into in a minute exactly why we haven't implemented either of those yet because there are two with each their own issues that we need to figure out but how it works is that first we must once we've agreed to play a game we must put out an initial shot and the prover needs to reactively see that shot and proved that it either is a hit or a miss to the hash that they have inputted on chain with their off chain computation so we have to have this first turn and it produces some perverse incentives that we'll talk about in a moment um we don't actually address them we assume honest actors in this game for now because it's a proof of concept but there are two different solutions uh and we'll get into them in a moment so the turn function takes this one parameter which is not passed into the proof which is used to access the data storage and then we have hit which is pretty much the only public input from our proof that the user gets to put in and we'll remember that for new game or join game we had one public input and board has one public input but shot has three public inputs we're gonna call shot three um a shot one even though it's those two numbers we're gonna consider shot and hash and hit the three public inputs that go into this zero knowledge proof and going into it we get our game out of storage we figure out the board hash that we're going to put into this proof the shot that we're going to put into this proof so you can think of if alice just played the first turn as the shot being alice's turn and the board being bob's board and then in the turn after this it will be the board of alice and the shot of bob and this will just increment or flip back and forth we convert uh the boolean hit um to a zero or one because circom only understands integers and then we pass it into the actual proof and here again this is just the zero knowledge and then the board hash and these shots both come from the game storage this board hash is from the game start and the shot is from the previous turn or first turn it it is never given in the parameters by the person proving the only thing they can do is assert whether or not it hit or not and that's where the trustless privacy comes in in our solidity so really you could technically close the video right here and call it a day but there's a lot more and what we do is given that we know now whether or not this hit is true there has been an off-chain computation that is verifiably computable and we now can trust it we increment the hit counter and we emit data for the subgraph just to know what happens so then we get to the point where we check if the game is over and if the game is over we're going to actually ignore this value next right here so if it's the very last turn you could put technically whatever you want and it doesn't matter but if the game is not over we're going to store that in our shots so that the next turn can take it out and inject it into the next proof so this is also another very important part of preserving the privacy while trusting that your opponent in this hidden information game is not lying then it just increments so that your the game knows where to go and finally we have the game over function and there's not really too much going on here so to be honest i'm not gonna talk much about it but it just sets the game state so that it's no longer playable and and set some winners and stuff you could totally at one point we actually had um both an nft that was given out and a um an erc20 wager so this is very modular and we hope that as you kind of watch this you start to get your own ideas of how you can inject hidden information into your l1 applications so now we've really gone over all of the solidity so we split this video into multiple parts which is why the continuity is probably a little weird but there should be three videos dropping at once so yeah go check out our discord that's going to be the best place for you to ask questions about this or any other builds that you want help with or just any discussion around zero knowledge but you can also subscribe to us here or follow us on twitter as we release more circon zero knowledge content in the future so check the description links to all the socials are there as well as links to all of the content referenced in this video so uh yeah see you in the next one
Up Next

13:08
Understanding Tornado Cash: DeFi Privacy via Zero-Knowledge Proofs
@smartcontractprogrammer
39.4K views•2021-08-27

53:55
Lens Protocol 101: Building Fullstack Social Apps with Digital Identity
@encodeclub
1.4K views•2023-09-14

64:25
Operational Security Essentials: A Guide for Hacktivists (OPSEC)
@hitbsecconf
157.4K views•2012-11-26

11:49
Understanding Ethereum: A Comprehensive Beginner's Overview
@99Bitcoins
3.1M views•2018-06-26
Related Study Plans & Knowledge Roadmaps
Structured learning paths in Blockchain & Crypto
blockchain-and-crypto
MPC Wallets: TSS, DKG & Secure Custody
01Foundations of Cryptography & Digital Signatures
02Secret Sharing & Introduction to MPC
03Distributed Key Generation (DKG)
+ 2 more learning modules
24h5 modules
Explore Roadmap
blockchain-and-crypto
ERC-4626: Yield Aggregators & Leverage
01Blockchain, Ethereum, and Solidity Foundations
02DeFi Primitives: Lending, Pools, and Yield Farming
03Mastering the ERC-4626 Tokenized Vault Standard
+ 3 more learning modules
35h6 modules
Explore Roadmap
blockchain-and-crypto
DePIN: IoT Registries, Proofs & Rewards
01Foundations of Blockchain & IoT
02Introduction to DePIN and the Flywheel Effect
03Designing IoT Device Registries & Secure Identity
+ 3 more learning modules
30h6 modules
Explore Roadmap
blockchain-and-crypto
Building EigenLayer AVS: Operators & Contracts
01Blockchain, Ethereum, and Smart Contract Basics
02Proof of Stake and Ethereum Staking
03Introduction to EigenLayer and Restaking
+ 3 more learning modules
24h6 modules
Explore Roadmap