






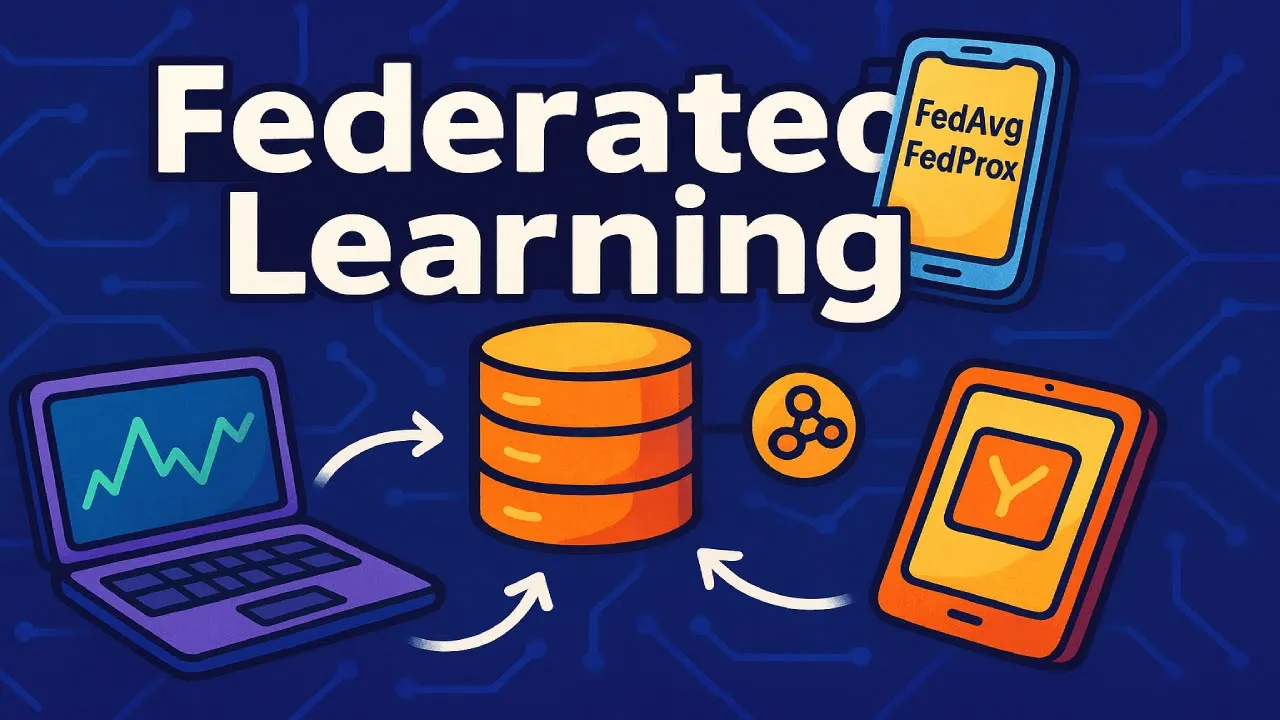









Federated learning is a decentralized AI training approach where the model is sent to the data rather than collecting data in a central server, enabling multiple parties to collaboratively train models using their own sensitive data while keeping the actual data distributed and private; this method was introduced by Google in 2016 to address data privacy concerns and comes in three forms: horizontal federated learning (similar datasets), vertical federated learning (complementary datasets), and federated transfer learning (adapting pre-trained models).
Federated Learning: AI Training Explained | Tutorial
Added:Basic concepts of Machine Learning (ML) model training, specifically gradient descent and weight optimization.
The fundamental differences between centralized data architectures and decentralized data storage.
Core network communication concepts, particularly client-server architectures and latency.
An introductory understanding of data privacy challenges and regulations (such as GDPR or HIPAA).
In-depth exploration of Federated Learning aggregation algorithms, such as Federated Averaging (FedAvg) and FedProx.
Studying security vulnerabilities in federated settings, including model poisoning, data reconstruction attacks, and defense mechanisms.
Integrating advanced privacy-preserving techniques like Differential Privacy (DP) and Secure Multi-Party Computation (SMPC).
Hands-on implementation of federated systems using specialized frameworks like TensorFlow Federated (TFF), PySyft, or Flower.
Analyzing industry-specific case studies, such as cross-device learning in mobile keyboards or cross-silo collaboration in healthcare networks.
47.2K views1.2Klikes6:27Original Release: 2023-07-07
Let's unpack the concept of federated learning. A method for training AI models that is all about keeping your sensitive data right where it should be with you. Now AI applications like chat bots, recommendation systems, and spam filters. They're all very data hungry and they have been fed tons of examples, mountains of information which they use to learn their specific tasks to build an AI model.
Now normally in machine learning we gather all of this data from different sources and bring it to one place. All of this will reside in a central server and that's where the actual training of the model takes place. Federated learning turns this process on its head.
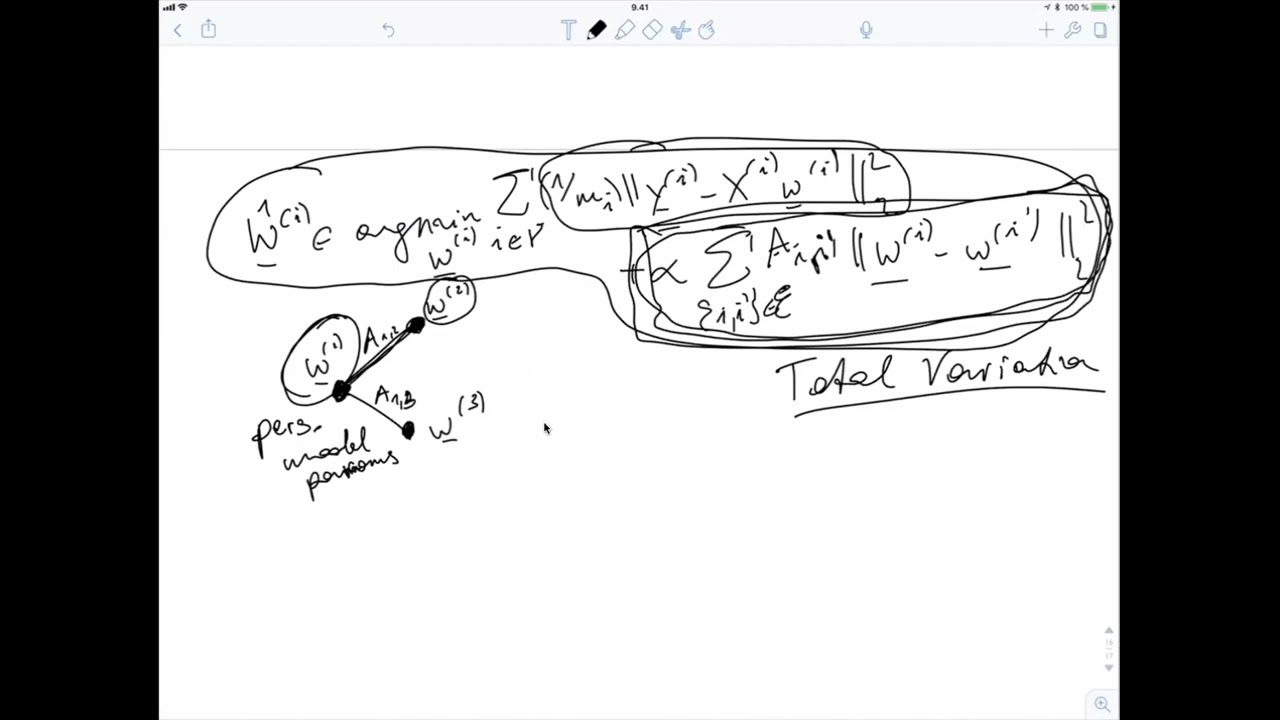
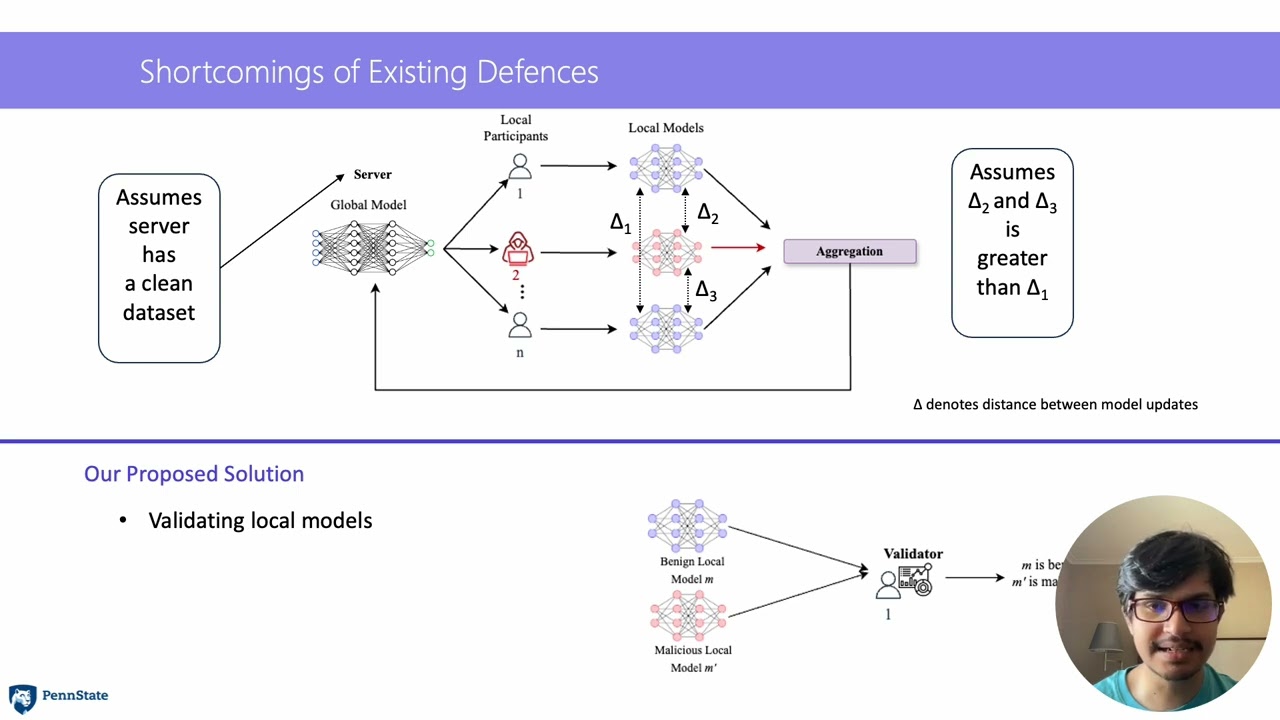
Instead of bringing the data to the model, we take the model to the data. So here's how it works. Think every device like a smartphone or a laptop or a server. It has its own local version of a model. So each of these are reporting into their own model and this model learns from the data right there on the device itself. Now after the model has learned from the local data, it sends only the model updates back to the central server, not the actual raw data.
So this all goes here to the central server. And then that server aggregates all of these updates from all the devices to create what is called the global model.
Now why bother with this level of decentralization?
Well, this concept was first introduced by Google in 2016 at a time when global attention was focused on the use and misuse of personal data. Concerns about data privacy and security prompted the search for alternatives to traditional centralized AI training methods, giving birth to federated learning. So let's imagine a scenario involving a group of companies that want to collaborate on building a model to predict market trends, but each company has sensitive sales data they want to keep private. So each company has access to an initial baseline predictive global model. Here's our global model up here. And this resides in a central server.
Now in their individual environments, each company trains the instances of the model using their own sensitive sales data. So we have the global model here and then these individual models with each company. And here is their sensitive sales data along the bottom.
And they're tweaking and refining their model based on their unique data. So the companies do not share their sensitive sales data. Instead, they only share the updates they made to the model. Now these updates, they don't contain any raw sales data, but they do reflect the insights gained from the data. The model updates are then sent back to the central server.
And here they're integrated into the global model. Now this iterative process continues with each company refining the model based on their private data and sharing only the model updates. Over time, this model becomes increasingly accurate at predicting market trends.
Even though no company had to share their sensitive data, each company benefits from the collective intelligence of the group while maintaining their data privacy. That is the essence of federated learning.
Allowing for collaborative learning from shared model updates while keeping the actual data distributed and private. Now we can think of federated learning as coming in three flavors. So there's horizontal and horizontal federated learning describes the forecasting model example we've just discussed where the data sets were all similar. In this case the similarity was this was all sales data.
Now another one is called vertical federated learning. So instead of using similar data sets we're dealing with complimentary data using movie and book reviews for example to predict someone's music preferences. And then the third kind is called federated transfer learning. Here we start with a model that's already been trained to do one task and then adapt it to do something slightly different like like how a pre-trained foundation model designed to perform a task like detecting cars is trained on another data set to do something else entirely like identify cats. Now the use cases for federated learning are farreaching and impactful. Just consider the healthcare industry where federated learning allows medical institutions to collaboratively train their models on their sensitive data without sharing the actual medical records or how financial institutions can improve their fraud detection mechanisms and credit scoring systems without compromising on customer privacy. However, federated learning is not without its challenges. There is the risk of inference attacks where adversaries may try to extract information about the data from the shared model updates when we've put them up there. Now to counter this, researchers are looking into strategies like secure multi-party computation to ensure privacy by encrypting model updates or by adding a degree of noise to the data to mislead potential attackers. Other challenges include computational efficiency because we do have all of this work going on locally here and maintaining transparency in model training and creating incentives for truthful participation. But in the end, federated learning offers a promising path towards a new generation of AI applications. By addressing privacy concerns and leveraging the power of distributed computing, federated learning holds the potential to revolutionize how AI models are trained.
If you have any questions, please drop us a line below. And if you want to see more videos like this in the future, please like and subscribe. Thanks for watching.
Up Next

62:49
Federated Learning: Train Models Across Devices Without Sharing Data
@mabdelfattah88
1.2K views•2022-03-30

73:14
3D Computer Vision: Lecture 1 Part 2 - Projective Geometry
@cvrplabatnus8618
15.3K views•2021-01-20

8:00
K-Nearest Neighbor Algorithm: Classification & Regression Guide
@IBMTechnology
106.1K views•2024-09-02

18:41
Neural Networks Explained: Math, Layers, and Learning Fundamentals
@3blue1brown
21.9M views•2017-10-05
Related Study Plans & Knowledge Roadmaps
Structured learning paths in Artificial Intelligence
artificial-intelligence
PINNs: Fluid Dynamics with PyTorch & DeepXDE
01Calculus & Fluid Dynamics Foundations
02Deep Learning & PyTorch Basics
03Introduction to Physics-Informed Neural Networks (PINNs)
+ 3 more learning modules
32h6 modules
Explore Roadmap
artificial-intelligence
Aligning LLMs: DPO, TRL & Custom Datasets
01Foundations of Python & Machine Learning
02Transformers and Large Language Models (LLMs)
03Aligning LLMs: SFT and RLHF
+ 3 more learning modules
24h6 modules
Explore Roadmap
artificial-intelligence
Federated Learning: PyTorch, Flower & Privacy
01Python & Machine Learning Foundations
02Deep Learning Basics with PyTorch
03Introduction to Federated Learning
+ 2 more learning modules
35h5 modules
Explore Roadmap
artificial-intelligence
Securing LLMs: Guardrails AI & NeMo Gateway
01Introduction to LLMs, Python, and APIs
02Understanding LLM Vulnerabilities & Threats
03Defending LLMs with Guardrails AI
+ 2 more learning modules
15h5 modules
Explore Roadmap