

















Linux Network Namespaces provide complete network isolation by creating separate, independent network environments on a single host, each with its own interfaces, routing tables, and forwarding tables; this isolation enables multiple virtual networks to coexist without interference, making namespaces essential for network virtualization in platforms like OpenStack, Mininet, and Docker, where they can be used to emulate hosts or isolate services such as DHCP processes for different tenants.
Linux Network Namespaces Explained: Mininet & OpenStack
Added:Basic Linux administration and command-line proficiency, particularly with network configuration tools in the 'iproute2' suite (e.g., 'ip link', 'ip addr').
Fundamental TCP/IP networking concepts, including subnets, routing tables, default gateways, and standard protocols like DHCP and ARP.
The concept of virtualization and OS-level virtualization, specifically how namespaces isolate resources in Linux.
Basic understanding of virtual networking components, such as virtual Ethernet (veth) pairs and network bridges.
Advanced Open vSwitch (OVS) features, including OpenFlow protocol configuration, flow tables, and network tunneling technologies (VXLAN, GRE).
Container Network Interface (CNI) architectures in Kubernetes (e.g., Calico, Flannel) that rely heavily on network namespaces for pod isolation.
Deep-dive into OpenStack Neutron architecture to understand how virtual routers, load balancers, and multi-tenant security groups are constructed.
Automating complex network topologies in Mininet using Python scripting to integrate with external SDN controllers like Ryu or ONOS.
132.8K views2.7Klikes25:51Original Release: 2015-07-01
this video is an introduction to Linux Network namespaces I'll start with a brief definition then I'll jump into two examples of using namespaces I'll walk through two labik scenarios that I believe will help make the video more practical you have the option to Simply watch the video or you can try the same setup on your own system at home the first example will mimic how minet Network emulation handles hosts the second will mimic how openstack provides DNS services to tenants the steps I take are all on a single VM running ubuntu14.04 with open V switch and the DNS mask service installed references here is a list of references and recommended resources related to this video links to these references are in the video description the network namespaces man page opv switch. org min. org a presentation on minet done at Stanford by Bob Lance and Brian oconor docs.
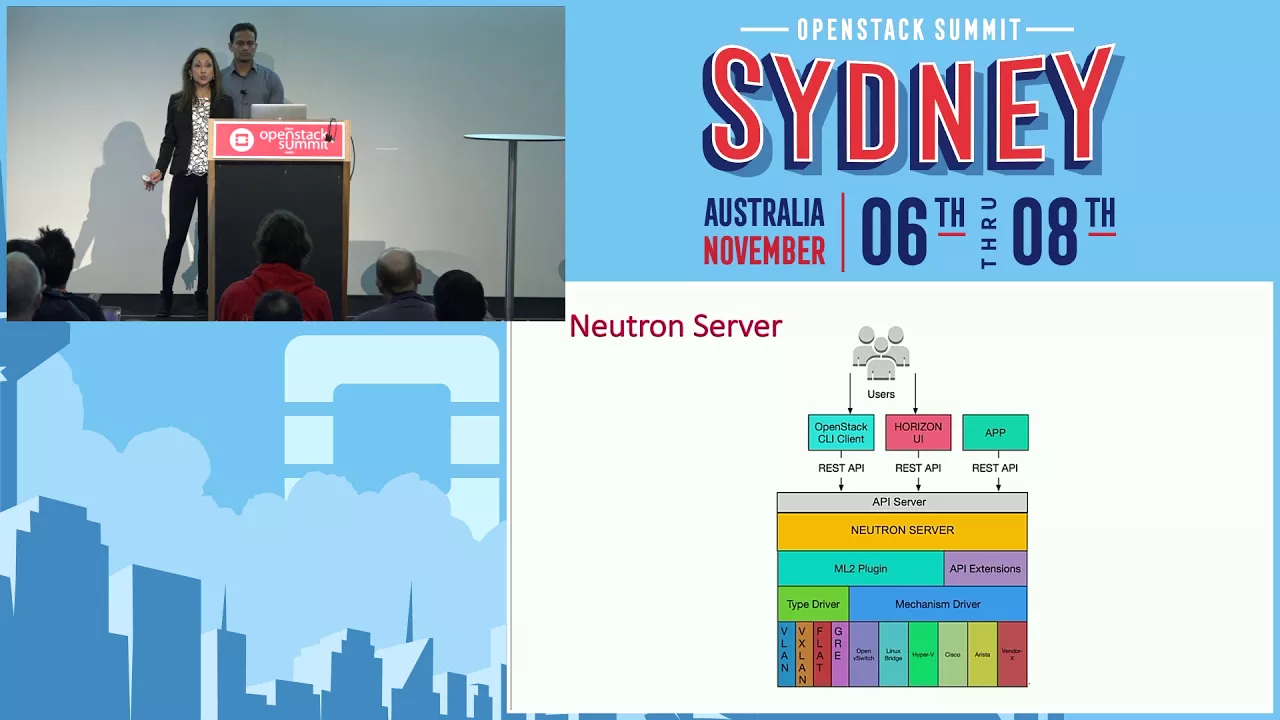
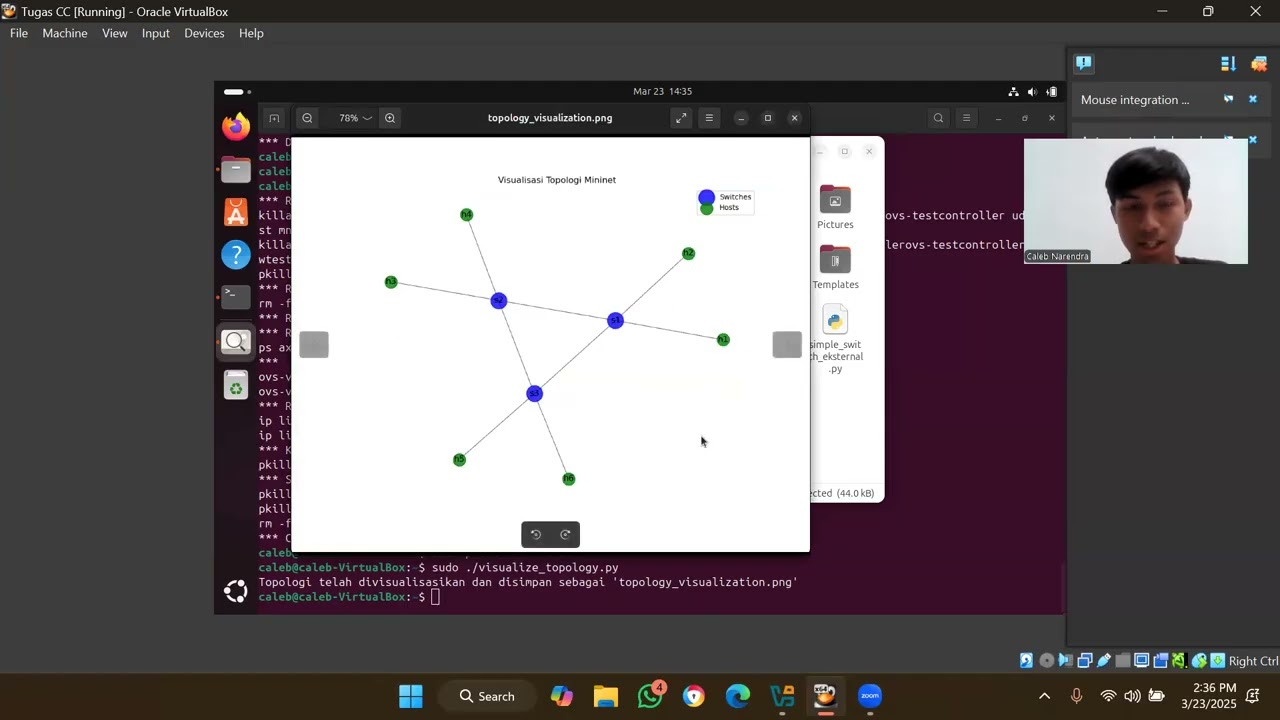
open.org specifically the neutron document and finally opencloud blog.com many Linux networking blog entries what are Linux Network Nam spaces Network namespaces allow there to be multiple isolated Network environments running on a single physical host or a single virtual machine each isolated Network environment has its own interfaces routing tables forwarding tables and network security isolation processes can be dedicated to an individual Network namespace to separate them from other namespaces network name spaces are used in openstack Linux containers Docker minet and more background on minet the first example using namespaces mimics what minet does automatically however we will do it in a manual way to learn about network namespaces if you're not already familiar with minet here is a brief explanation minet software allows you to launch custom virtual Network topologies all within a single virtual machine or a single physical host its range of applications includes learning testing and teaching about software defined networking as well as networking in general for more detail about minet you should go to Min net.org you can also watch my introduction to minet video on my YouTube channel for the purposes of this video I'll mimic what minet does to emulate the simplest topology this topology will have two hosts connected together through one instance of open V switch this is done on my single VM the two emulated hosts will have their own network environment thanks to network name spaces this setup was demonstrated in a presentation by Bob Lance and Brian oconor at a Stanford Network seminar which I'll link to in the video description the root Network Nam space we start with taking a look at the root name space this is just the default Network environment you see when working on a Linux system this will be kind of like our canvas that we're going to put our virtual Network on top of so there's nothing new here yet we will just take a look at my vm's root Network namespace before adding new network namespaces to look around I will use some IP Route 2 based commands this is instead of using the older net tools based commands like if config route and ARP so in the standard root namespace IP Link shows there's just a loot back interface and an e to zero interface IP address or just IPA shows the e zero interface has an IP address of 192.168.1.10 Ip route displays the routing table adding Network Nam spaces now let's add two new network namespaces each of these namespaces will represent a single host in our Network topology IP netns add red IP netns add green I've just added two new network namespaces named red and green IP netns by itself displays those two new namespaces also if we look in the directory /var run/ netns we can see the namespaces listed there as well if we wanted to delete a namespace we'd say deel for delete instead of add I won't delete the new network name spaces here here though looking at The Logical diagram now we have the two new network namespaces red and green red and Green's Network environments are isolated both from each other and from the root namespace to look further we can use the IP netns exec command so IP netns exec red IP Link with this command we are simply running the IP Link command however instead of running this in the root namespace we are executing it directly in the red namespace in red there is only a loop back interface and it is down checking green as well shows the same situation IP netns exact green IP Link to emulate a simple Network in a manner like minet does we want to connect these namespaces into a virtual switch in this case we will use open V switch our instance of open V switch will be in the root namespace ovs vs Kettle or vctl add- brr ov1 this starts a new virtual switch that I've named ov1 by the way if you'd like more background about open V switch I recommend going to opv switch. org also you can watch my introduction to open V switch video on my YouTube channel so we now have ovs one we can check that with ovs-vsctl we will use V pairs or virtual ethernet interfaces V pairs act like a pipe anything that goes in one end of the pipe simply comes out the other end we can use V pairs to cross Network namespaces IP Link add eth z-r type v p or name v-r this IP Link command creates a v pair one endine of it I'm choosing to name eth z-r this end we're going to put into the red namespace the other end of our new V pair I've named v-r this end we will connect to our ovs instance in the root namespace what has happened now is there is this V pair which can be visualized as a pipe at the moment we haven't connected the two ends of it to anything with IP Link we can see both ends of the V pair sitting in our root namespace we want to connect one end of this pipe to the red namespace and the other end to our open V switch instance IP Link set eth z-r netns red this command places the end named eth z-r into the red namespace IP Link shows we can no longer see the interface e z-r in the root namespace that is because it is now in the network isolated red namespace let's run the command IP Link in the red namespace IP netns exact red IP Link here we can see the end of the re pair we named as eth z-r is now located in the red namespace now let's connect the other end of our re pair to ovs ovs vsk Kettle add port ov1 v-r this ov- vs Kettle command attaches the other end of the V pair named v-r to ovs one running ovs vs Kettle show we can see there is a v-r attached to ovs one now we have the red namespace connected to the ovs instance the same thing will be done for the green name space to connect it to ovs as well IP Link add e-g type V perer name v-g this creates another new virtual ethernet pair or V pair one side is named eth z-g the other side is named v-g IP Link set eth z-g netns green this puts the end named eth z-g into the green namespace ovs vs kle add Port ov1 v-g this attaches the end named v-g to ov1 now the two name spaces have a path to each other via open V switch configuring interfaces and network namespaces now that everything is connected together we need to turn all the interfaces up and we need to assign IP addresses let's start with the link to the red namespace one side this V pair is on ovs one however it is down I'll turn it up with IP Link set v-r up now we need to work inside the red namespace and execute IP Link commands there to turn up Loop act 0 and eth z-r IP Nets exac red IP Link set Dev l0 up IP netns exact red IP Link set device eth z-r up e z-r needs an IP address IP net ands exac red IP address add 10.0.0 1/24 Dev e-r this assigns the IP address 10.0.0 1/24 to e-r IP netns EXA red IPA shows the two interfaces they are up and the expected IP address is assigned IP Nets exact red IP route shows the red namespace now has a route for 10.0.0 24 via its interface eth z-r back in the root name space running IP route shows the root namespace doesn't have any awareness of 10.0.0.0 sl24 this is as expected since the routing of the red namespace is isolated from the root namespace now we will do the same procedure for the green namespace except we'll want to assign 10.0.0 two for it IP Link set device v-g up this turns up the end of the V pair attached to obs1 now I'll show a bit of a shortcut to work inside the green namespace instead of using the IP netns exec green command over and over we can simply start a bash shell within the green namespace IP netns exec green bash now we are in the green namespace instead of the root namespace and can use regular IP commands we no longer have to preface every command with IP netns exec green IP Link set Dev l o up IP Link set de eth z-g up these commands turn up the interfaces Loop back0 and eth z-g in the green namespace finally we assign the IP IP address at 10.0.0 2/24 Dev eth z-g now the eth z-g port has IP 10.0.0 two which you can see with IPA remember that we are working directly in the green namespace since we ran ipet NS exact green bash so to get back to the root name space we would just type exit final State the final state is there are two network name spaces red and green in the root Nam space is an ovs instance named ovs 1 the green and red Nam spaces are linked together to ovs one through V pairs ovs one acts as a layer 2 switch enabling connectivity between the two Nam spaces we can confirm connectivity between red and green with a ping ping 10.0.0 two the end result here is we have two emulated hosts connected through open V switch we could continue this experiment and connect our ovs instance to an sdn controller however for our purposes here which is learning about network name spaces we will leave it at that now we will move on to our second scenario this one is related to open stack we will connect Network Nam spaces without using beef Pairs and we will run processes within Network namespaces DHCP in openstack openstack is well known as a popular open source platform to deploy Cloud infrastructures here we will mimic one small piece of openstack providing DHCP services to tenants in the cloud in the cloud we have individual physical nodes that are responsible for providing many DHCP processes one for each virtual network of every tenant when we have all these dhtp processes running on individual hosts these processes need to be isolated we can use network name spaces for that isolation to mimic this behavior from open stack we will build on the previous minet example keep in mind that in a real openstack deployment there would be a hypervisor like KVM and real VMS versus our emulated hosts so we start with the two name spaces red and green which are emulating two hosts VLAN separation first the two name spaces red and green will be isolated from each other in this scenario red and green will represent two different tenants in the cloud since they are both connected to the same open V switch instance vlans will be used an open V switch to keep them isolated ovs vs Kettle set Port v-r tag equals 100 ovs vs Kettle set port v-g tag equals 200 these ovs vs Kettle commands changed vlans on the two ports connecting to the two name spaces the first one moved port v-r to VLAN 100 the second one moved v-g to VLAN 200 looking at the updated diagram we see the name spaces are now isolated by vlans also we want to remove the current Network namespace IP addressing since we'll use DHCP instead IP netns exec red IP address deel 10.0.0 1/24 Dev e z-r IP net ands exac green IP address de 10.0.2 24 Dev e-g these commands are executed in the respective namespaces and remove the configured IPS add network name spaces now I'll add two new network name spaces these will host the DHCP processes for two tenants IP Nets add dhp dasr IP Nets add dhtp DG the first namespace dh- R will be used for the red tenant the second one DHCP DG will be used for the green tenant open V switch internal ports earlier to connect red and green to open V switch in the root name space we used V pairs for dh- and dh- green namespaces we will connect through open V switch internal ports first let's work with the connection to dh- ovs vsk kle add- Port obs1 tap- R this creates a new Port named tap- r on ovs ovs vs Kettle set interface tap- R type equals internal this makes this new Port an internal Port obvs Kettle set Port tap- R tag equals 100 this places the port into VLAN 100 let's set up the port for green ovs vsk kle add- Port obs1 tap- G creating the port named tap- g ovs v Kettle set interface tap- G type equals internal making the New Port of type internal ovs vs Kettle set Port tap- G tag equals 200 putting the port in VLAN 200 OBS vs Kettle show confirms our configuration so far there are the two new internal ports named tap dashr and tap- G in VLS 100 and 200 respectively looking at the diagram there are two new internal ports however they are sitting in the root namespace still they need to be moved to the right namespaces IP Link set tap- R netns dh- this command moves the port tap- R into the dh- r namespace IP Link set tap- G netns dhp DG this command moves the port tap- g into the dhtp DG namespace IP Link in the global namespace confirms we can no longer see dhtp DG and dhtp since they've been moved even though we can't see the ports in the root namespace we can still see them on ovs ovs-vsctl show and here is the updated diagram interface configurations now we will turn up interfaces and assign IPS in the new namespaces dh- and dhpg let's go directly into the bash shell for the namespace dh- with IP netns exec dhp bash IP Link set Dev L up IP Link set Dev tap- up turning up the loop back interface and the tap- r interface in the namespace dhp D IP address add 10.50 15224 art Dev tap- R now 10.50 52/24 has been assigned to interface tap- R in the dh- namespace we will do the same for dhpg IP netns exec dhpg bash IP Link set Dev L up IP Link set Dev tap- G up IP address add 10.50 15224 Dev t-g and adding IP address 1050 do502 to the tapg interface in [Music] dhpg note here how I intentionally use the exact same IP addresses in the two Nam spaces dhpg and dh- R this is to demonstrate that these two environments are isolated from one another and don't interfere this this is what one would expect in a cloud environment we want each tenant to use any private IP addressing they care to use and for it to be isolated from other tenants overlapping IPS are fine due to the isolation provided by Network namespaces and [Music] vlans running a process in a network namespace finally we want to run dhp for DHCP we use the DNS mask service we want to have two DNS mask Services running one for the red tenant and one for the green tenant these need to be isolated from one another therefore we use the IP Nets exec command yet again ipets exec d-r DNS mask D- interface equals tap- r-- DCP range equals 10.50.10 comma 10.50 50100 comma 255.255.255.0 this starts DNS mask but within the dh- namespace DNS mask runs on the tap- interface and uses a pool in this range now the exact same command again except it is in the dh- G namespace so I'll make those changes here I've now started two DNS mask processes that are using the same range of ips for a dhtp pool however they are isolated from one another the first process is running in the dh- r namespace the second in the dhpg namespace we can actually validate this by the process IDs ps- EF shows pids 3162 and 3165 for the two DNS mask processes IP netns identify 3162 shows process 3162 is in the d-r namespace as expected and IP netns identifi 3165 shows that the PID 3165 is in the dhp DG namespace also as expected let's see that this all worked all right by pulling IPS for our clients first for the red namespace IP netns exec red dhclient e z-r this seems to have completed IP nin exact Red IPA shows we indeed have received an IP address assigned by The dnes Mask service for the red tenant now the same for the green tenant again we see this has worked one last check of the diagram to see that DNS mask is now running in two different name spaces and our emulated tenants red and green were able to to receive IP addresses by isolated dhp processes final review I'll close now with a final review of what has been discussed this should help solidify all the concepts we walk through in this video before that final review a request for you the viewer if you found this video to be helpful please subscribe to this channel for more like it also to contact me directly I can be found at linkedin.com davidm review this video covered Linux Network namespaces and described some ways they can be used first we mimicked how minet builds emulated Network typologies we created two isolated Network namespaces red and green we created virtual Ethernet or V pairs to connect these namespaces through an ovs instance running in the root namespace we turned up interfaces and assigned IP addresses in the namespaces then we demonstrated reachability between red and green we also saw that the root name space had no knowledge of the layer 3 addressing used by the network namespaces after this we mimicked how open stack provides dhdp services to tenants in the cloud we turned our name spaces red and green into isolated environments by assigning vlans on the ovs side of the V pairs then two new namespaces were created to host two isolated DHCP processes these Nam spaces were connected to ovs by creating ovs internal ports moving those ports to the appropriate vlans and finally by moving these ports directly into respective name spaces lastly it was demonstrated that the tenants were able to acquire IP addresses from separated DNS mask processes running in individual Network namespaces that wraps up this video and thank you for watching
Up Next

15:45
Optimizing Docker Container Startup with Go Runtime LockOSThread
@OpenInfraFoundation
160 views•2023-06-29

87:26
Introduction to Secure Multiparty Computation with Yehuda Lindell
@fhe_org
7.7K views•2021-02-04

4:55
HTTP Requests Explained: GET, POST, PUT, DELETE
@codecademy
103.1K views•2021-10-07

19:25
Enigma Machine Mechanics: WWII Encryption Explained
@JaredOwen
13.2M views•2021-12-11
Related Study Plans & Knowledge Roadmaps
Structured learning paths in Computer Science
computer-science
Container Runtimes: Namespaces, Cgroups & Go
01Linux Systems & Go Programming Foundations
02The Core of Isolation: Chroot and Filesystems
03Linux Namespaces: Process Isolation
+ 3 more learning modules
32h6 modules
Explore Roadmap
computer-science
Building a CHIP-8 Emulator: Rust & CPU Basics
01Computer Architecture Foundations (Bits & Bytes)
02Rust Programming for Systems Development
03CHIP-8 Virtual Hardware Specifications
+ 2 more learning modules
32h5 modules
Explore Roadmap
computer-science
Building BitTorrent: Go, P2P & Concurrency
01Go Fundamentals & Concurrency
02Networking Foundations & P2P Architecture
03Bencode Parsing & Torrent Metadata
+ 3 more learning modules
26h6 modules
Explore Roadmap
computer-science
Actor Models (C++ Concurrency & Lock-Free)
01C++ Multi-Threading Foundations
02Thread Pools and Task Scheduling
03Atomics and Lock-Free Queue Design
+ 3 more learning modules
45h6 modules
Explore Roadmap