













OAuth 2.0 is a security protocol that enables third-party applications to access specific user data without exposing login credentials, using an authorization code flow where users grant permission, the authorization server issues an access token, and the client uses this token to request resources from the resource server, with optional refresh tokens for token renewal and revocation capabilities for enhanced security.
OAuth 2 Explained: A Simple Guide to Access Delegation
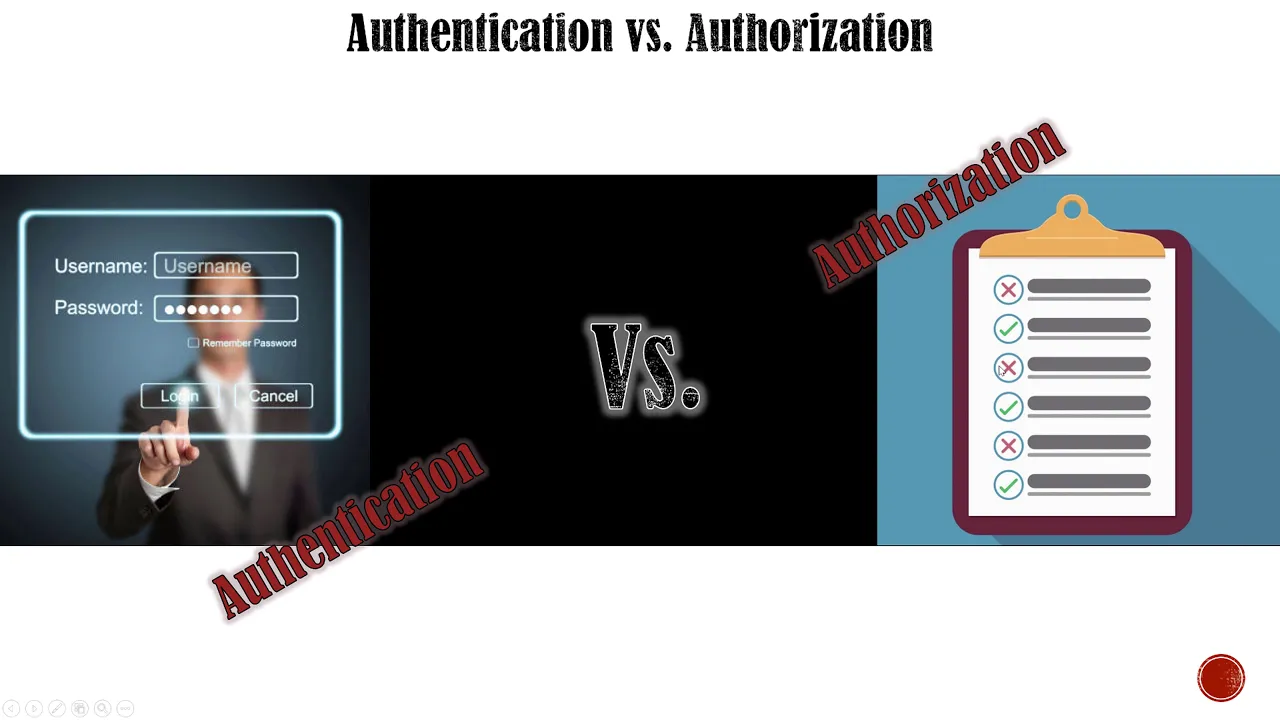
Added:The conceptual difference between Authentication (verifying who a user is) and Authorization (determining what a user can access).
Basic knowledge of the HTTP protocol, including standard request/response structures, query parameters, headers, and HTTP redirects.
A foundational understanding of APIs (Application Programming Interfaces) and how third-party services exchange data.
An awareness of basic cryptographic concepts, such as symmetric/asymmetric encryption and the role of HTTPS in securing web communication.
Exploring OpenID Connect (OIDC), an identity layer built on top of the OAuth 2.0 framework to handle authentication.
Understanding the Proof Key for Code Exchange (PKCE) extension, which secures the authorization code flow for mobile and single-page applications.
Analyzing the structure, generation, and validation of Access and ID tokens, specifically focusing on JSON Web Tokens (JWT).
Studying OAuth 2.0 security best practices, including threat modeling, token revocation, token rotation, and defense against common vulnerabilities like CSRF and redirect URI manipulation.
762.4K views17.5Klikes4:32Original Release: 2023-06-29
[Music] have you ever tried wrapping your mind around o off2 but ended up lost in the sea of jargons that's why we're here today we're breaking down these complex Concepts into digestible explanations let's Dive Right In imagine the early days of the internet sharing info was straightforward just hand over your username and password to another service and they could access anything they wanted this practice is fry upon these days but we might still encounter this practice in certain personal finance software to scrape information from crusto Banks luckily we have something much better these days enter OA 2 OA 2 is like giving someone a special key this key allows them to access specific information in another application we control who gets access to our data without having to share a password and yes we can revoke that key at any time now let's play this out with an example consider a photo storage application Snap Store we've been using it to store our photos and now we want to print some of them using a thirdparty printing service PR magic instead of manually uploading each photo to PR magic we ask PR magic to do the job with a simple click we Grant PR magic permission to access our photos on Snap Store using o Off 2 preager can then access our Snap Store photos on our behalf without ever knowing our Snap Store login credentials this is an example of the O off flow is an elegant stance between us Prem magic and snap store all orchestrated by o of2 now let's unpack this further in this context we are the resource owner because we own our photos on Snap Store Snap Store is the resource server that stores our photos pre magic is the client that wants to access the photos the authorization server could be a part of snap store or an external identity provider and is responsible for handling the O off2 process let's follow the oof2 flow in this scenario it begins when we instruct pre magic to fetch photos from Snap Store pre magic sends a client ID and scope which represent the access level requested to snap store's authorization server as a resource owner we authenticate directly with SNAP store and Grant Prem magic the consent to access our photos once consent is granted the authorization server sends an authorization code back to PR magic Prim magic then presents this authorization code is client ID and client secret to the authorization server now the client secret is a private key shared only between PR magic and the authorization server if the authorization server verifies the authorization code client ID and client secret IT issues an access token to PR magic finally Prim magic uses this access token to request our photos from snap store's resource server this all off to process ensures that our Snap Store login credentials are never exposed to pre magic while allowing pre magic to access only the photos we authorized it to see it's also important to note that the access token can be set to expire after a certain time or can be revoked by us at any point providing an additional layer of security oa2 also support refresh tokens which can be used to obtain a new access token when the o one expires without requiring our in ition that's o off to in a nutshell is an essential piece of the web security infrastructure and the backbone of many secure Seamless app interactions we use daily if you like our videos you may like our system design newsletter as well it covers topics and Trends in large scale system design trusted by 400,000 readers subscribe that blog.
byby go.com
Up Next
57:18
Implementing Google OAuth 2.0 in Node.js: A Practical Guide
@TomDoesTech
112.5K views•2021-10-26

26:22
Walking in the City: Urban Rituals and the Flâneur in Contemporary India
@PSBTIndia
1.9K views•2016-08-02

9:49
FastAPI vs Flask vs Django: Choosing the Right Python Web Framework
@TechWithTim
302.5K views•2024-05-26

1:42
Game of Thrones Opening Credits: A Cinematic Analysis
@gameofthrones
46.3M views•2011-04-18
Related Study Plans & Knowledge Roadmaps
Structured learning paths in General & Interdisciplinary Studies
general-studies
Artificial Light: History, Tech & Human Impact
01The Pre-Electric Era: Fire, Oil, and Gas Lighting
02The Incandescent Revolution and Grid Electrification
03Gas Discharge and Fluorescent Illumination
+ 3 more learning modules
14h6 modules
Explore Roadmap
general-studies
Elevator Engineering: History, Physics & Cities
01From Hoists to Safety Brakes: The Dawn of Vertical Lift
02Hydraulic vs. Traction: The Engineering Physics of Elevators
03Modern Speed, Safety, and Algorithms
+ 2 more learning modules
12h5 modules
Explore Roadmap
general-studies
Rubber: Material Science, History & Geopolitics
01Origins of Natural Rubber & Mesoamerican History
02The Chemistry of Natural Rubber & Vulcanization
03The Geopolitics of the Rubber Boom & Colonization
+ 2 more learning modules
12h5 modules
Explore Roadmap
general-studies
Containerization: Evolution, Logistics & Trade
01Ancient Trade & Bulk Cargo: Amphorae to Barrels
02The Industrial Revolution & Cardboard Packaging
03The Containerization Revolution: Malcom McLean
+ 2 more learning modules
12h5 modules
Explore Roadmap